
The cybersecurity landscape is currently locked in a deeply uncomfortable transitional phase. We have reached a point where highly capable artificial intelligence models are readily accessible to threat actors, drastically lowering the cost, time, and effort required to discover zero-day exploits.
Meanwhile, the people tasked with defending our critical networks are still relying on painfully slow, human-bottlenecked triage processes.
It is a fundamental asymmetry in the digital battlefield. When a threat actor finds a flaw, they can exploit it almost immediately. When a defender finds one, they have to manually verify the risk, develop a patch, and schedule system downtime.
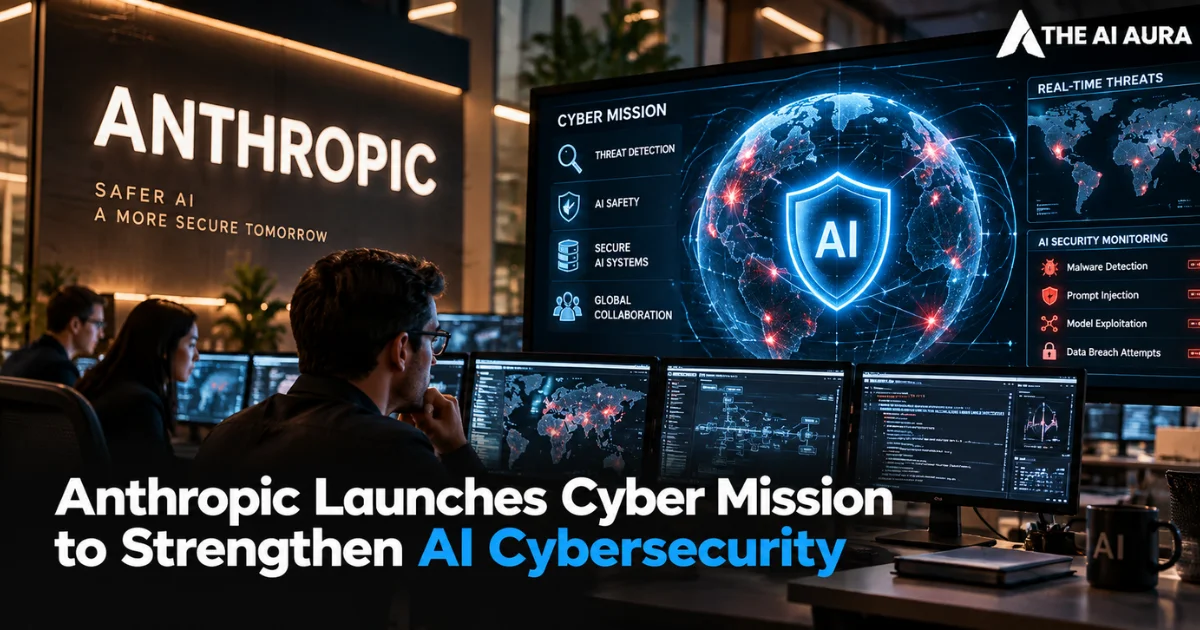
This structural friction is exactly what Anthropic is targeting right now. By launching their sweeping Cyber Mission, the AI lab is acknowledging a hard truth about their own technology.
As examined in AI + Cybersecurity: How Hackers and Defenders Are Using AI in 2026, generative models are currently giving attackers a massive advantage, and without aggressive, well-funded intervention, the defense is going to lose critical ground.
Hardening the Grid and Physical Infrastructure
The most terrifying vulnerabilities in our modern world do not live in your web browser or your smartphone. They live in operational technology. This is the aging, highly proprietary software running our power grids, water treatment plants, manufacturing facilities, and rail networks.
Securing these physical environments is notoriously difficult because you cannot simply take a municipal water system or a regional power station offline for a routine software update.
Known vulnerabilities routinely sit unpatched for years simply because the operational risk of applying a fix is deemed higher than the theoretical risk of a cyberattack.
Anthropic is attempting to dismantle this hesitation through their new Critical Infrastructure Defense Program. Rather than just offering an API key, they are pairing their most advanced Claude models with on-site deployment engineers.
More importantly, they are not trying to navigate this complex sector alone. They are partnering with established security and industrial heavyweights like Dragos, CrowdStrike, and Rockwell Automation.
By doing so, they place their frontier models directly into the hands of the operators who already manage these fragile industrial networks on a daily basis.
According to Anthropic’s internal roadmap for the project, the immediate objective is to work alongside these trusted providers to figure out exactly which AI deployment strategies actually succeed in the field.
The goal is to catch and repair weaknesses long before an adversary can leverage them to cut off regional power or compromise drinking water safety. It is a massive logistical undertaking, but injecting heavy computational analysis into operational technology is the exact force multiplier these exhausted security teams require.
Automating Open-Source Security Triage
The second major pillar of this initiative addresses the hidden backbone of the modern internet. Almost all enterprise software relies heavily on open-source code, which is largely maintained by underfunded and overworked volunteer developers.
Finding a bug in these massive codebases is incredibly easy today but figuring out if that bug is actually exploitable takes hours of human labor that most open-source projects simply do not have to spare.
To bridge this specific gap, the company has introduced the OSS Scanner. This tool essentially weaponizes frontier models for the defense.
Instead of just dumping a massive, unactionable list of theoretical vulnerabilities on a stressed project maintainer, the system generates a working proof of concept for the exploit alongside a highly specific suggested code fix. It ships these comprehensive reports automatically, bypassing the traditional human review cycle entirely.
While that means a few false positives or misjudged severity ratings will inevitably slip through, the sheer speed of delivery makes it a highly favorable trade-off.
From an analytical perspective, this is the most pragmatic application of artificial intelligence in cybersecurity I have seen this year. Understanding these vulnerabilities is critical, much like managing foundational application risks outlined in our guide to AI Security Explained: Prompt Injection, Data Leaks & How to Prevent Them.
The leadership at Anthropic forecasts that within two years, AI will inherently favor the defense by making it easier to write fundamentally secure code from scratch. Until we reach that tipping point, however, the barrier to exploiting systems will remain dangerously low.
This new strategy recognizes that the only way to survive our current vulnerability gap is by ruthlessly automating the grueling, manual work of threat disclosure and patching. It represents a vital industry shift from passive threat analysis to active, automated defense.